What's New in v0.5
April 10, 2020
A framework for secure and scalable network traffic analysis. Convert packet streams into type-safe structured audit records for machine learning and security research.
Inside the product
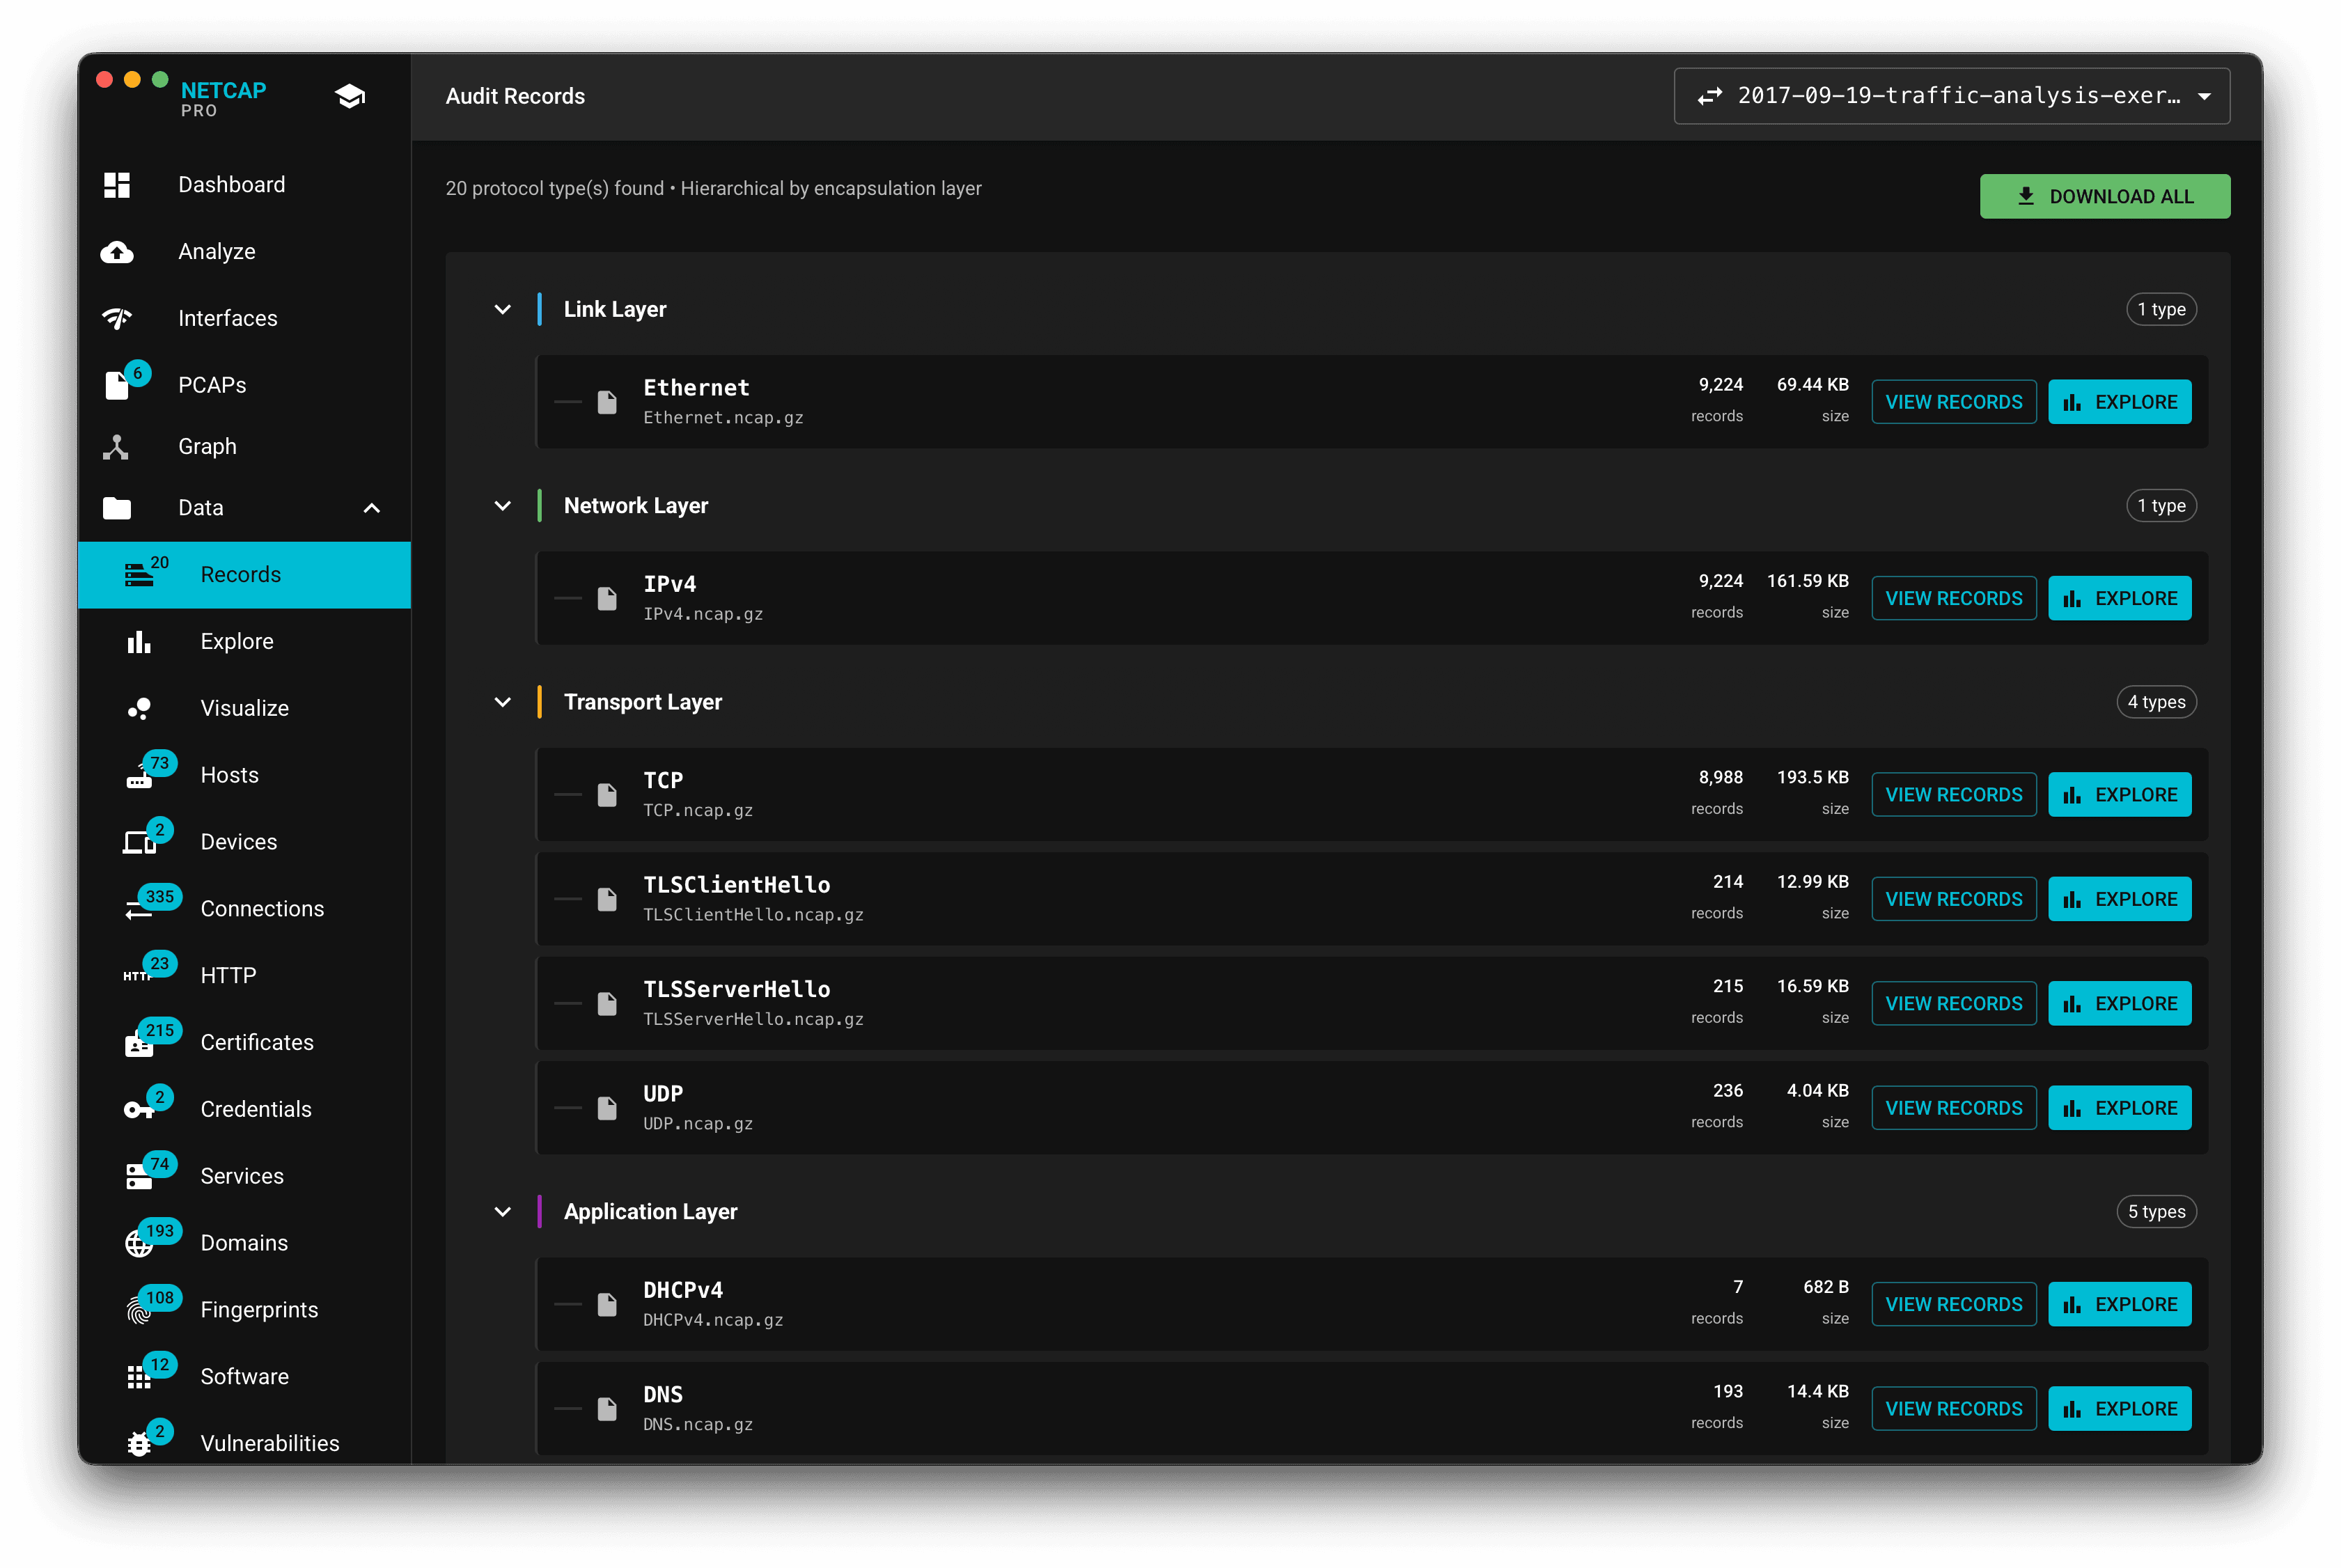
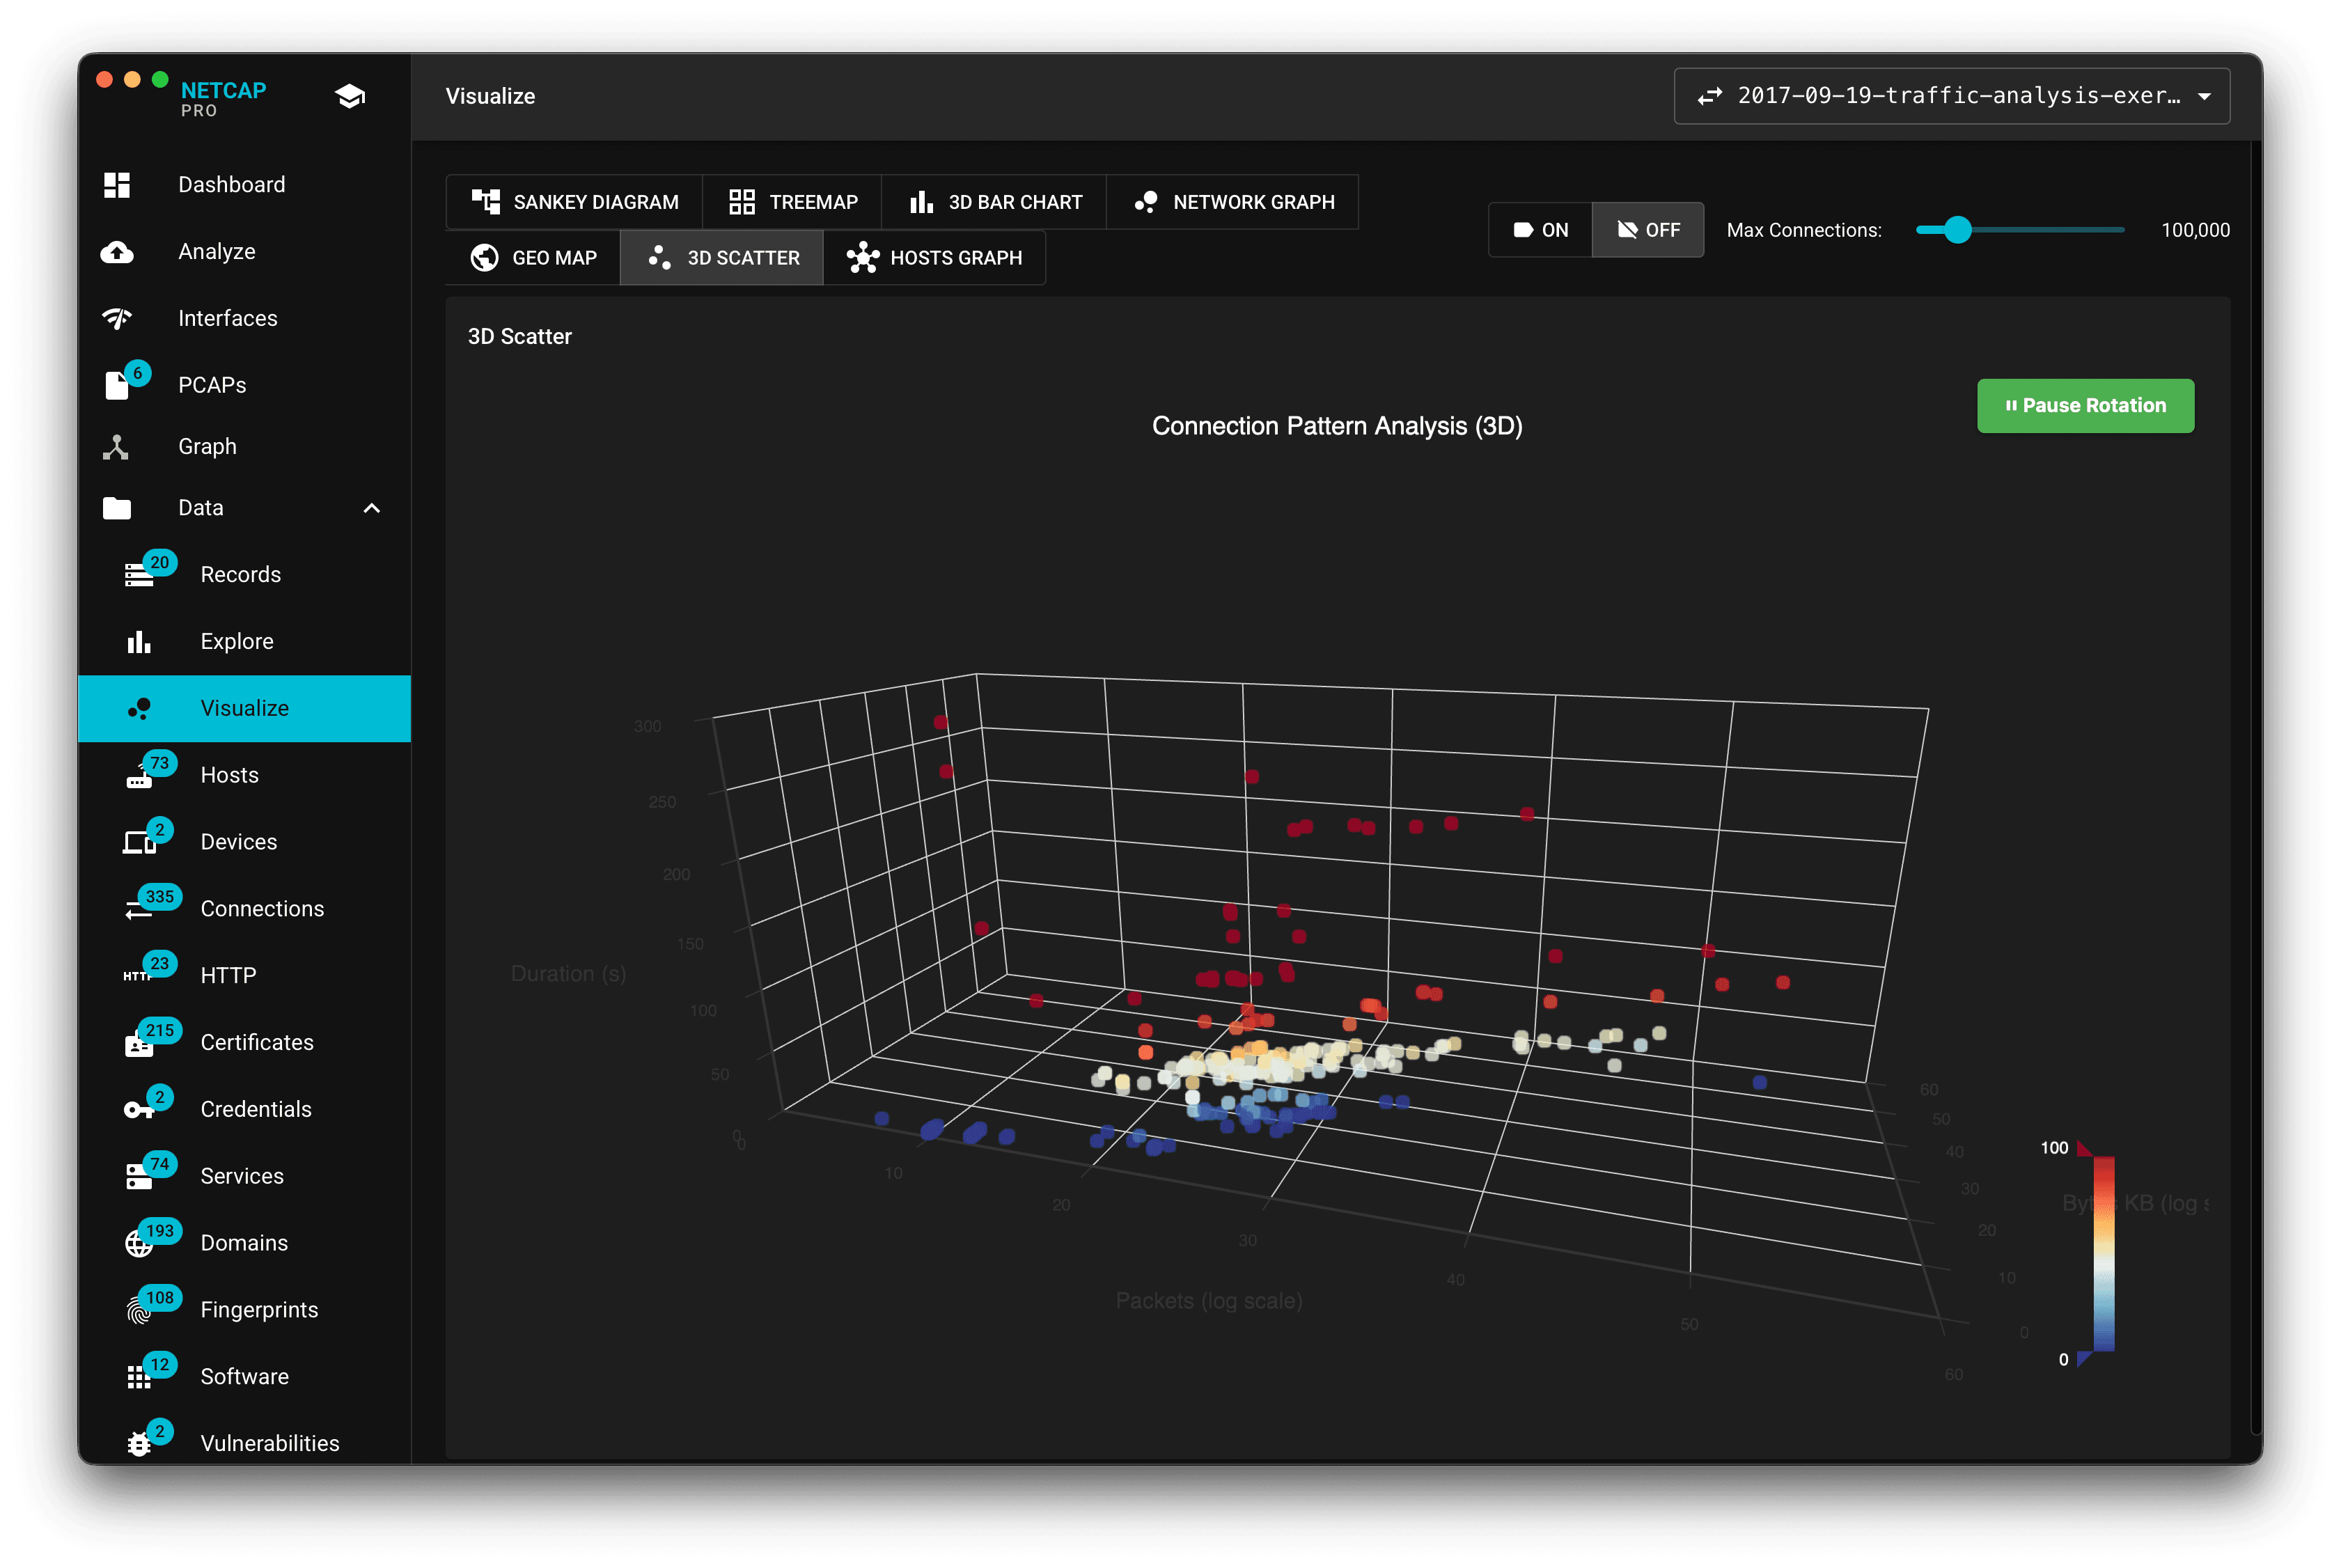
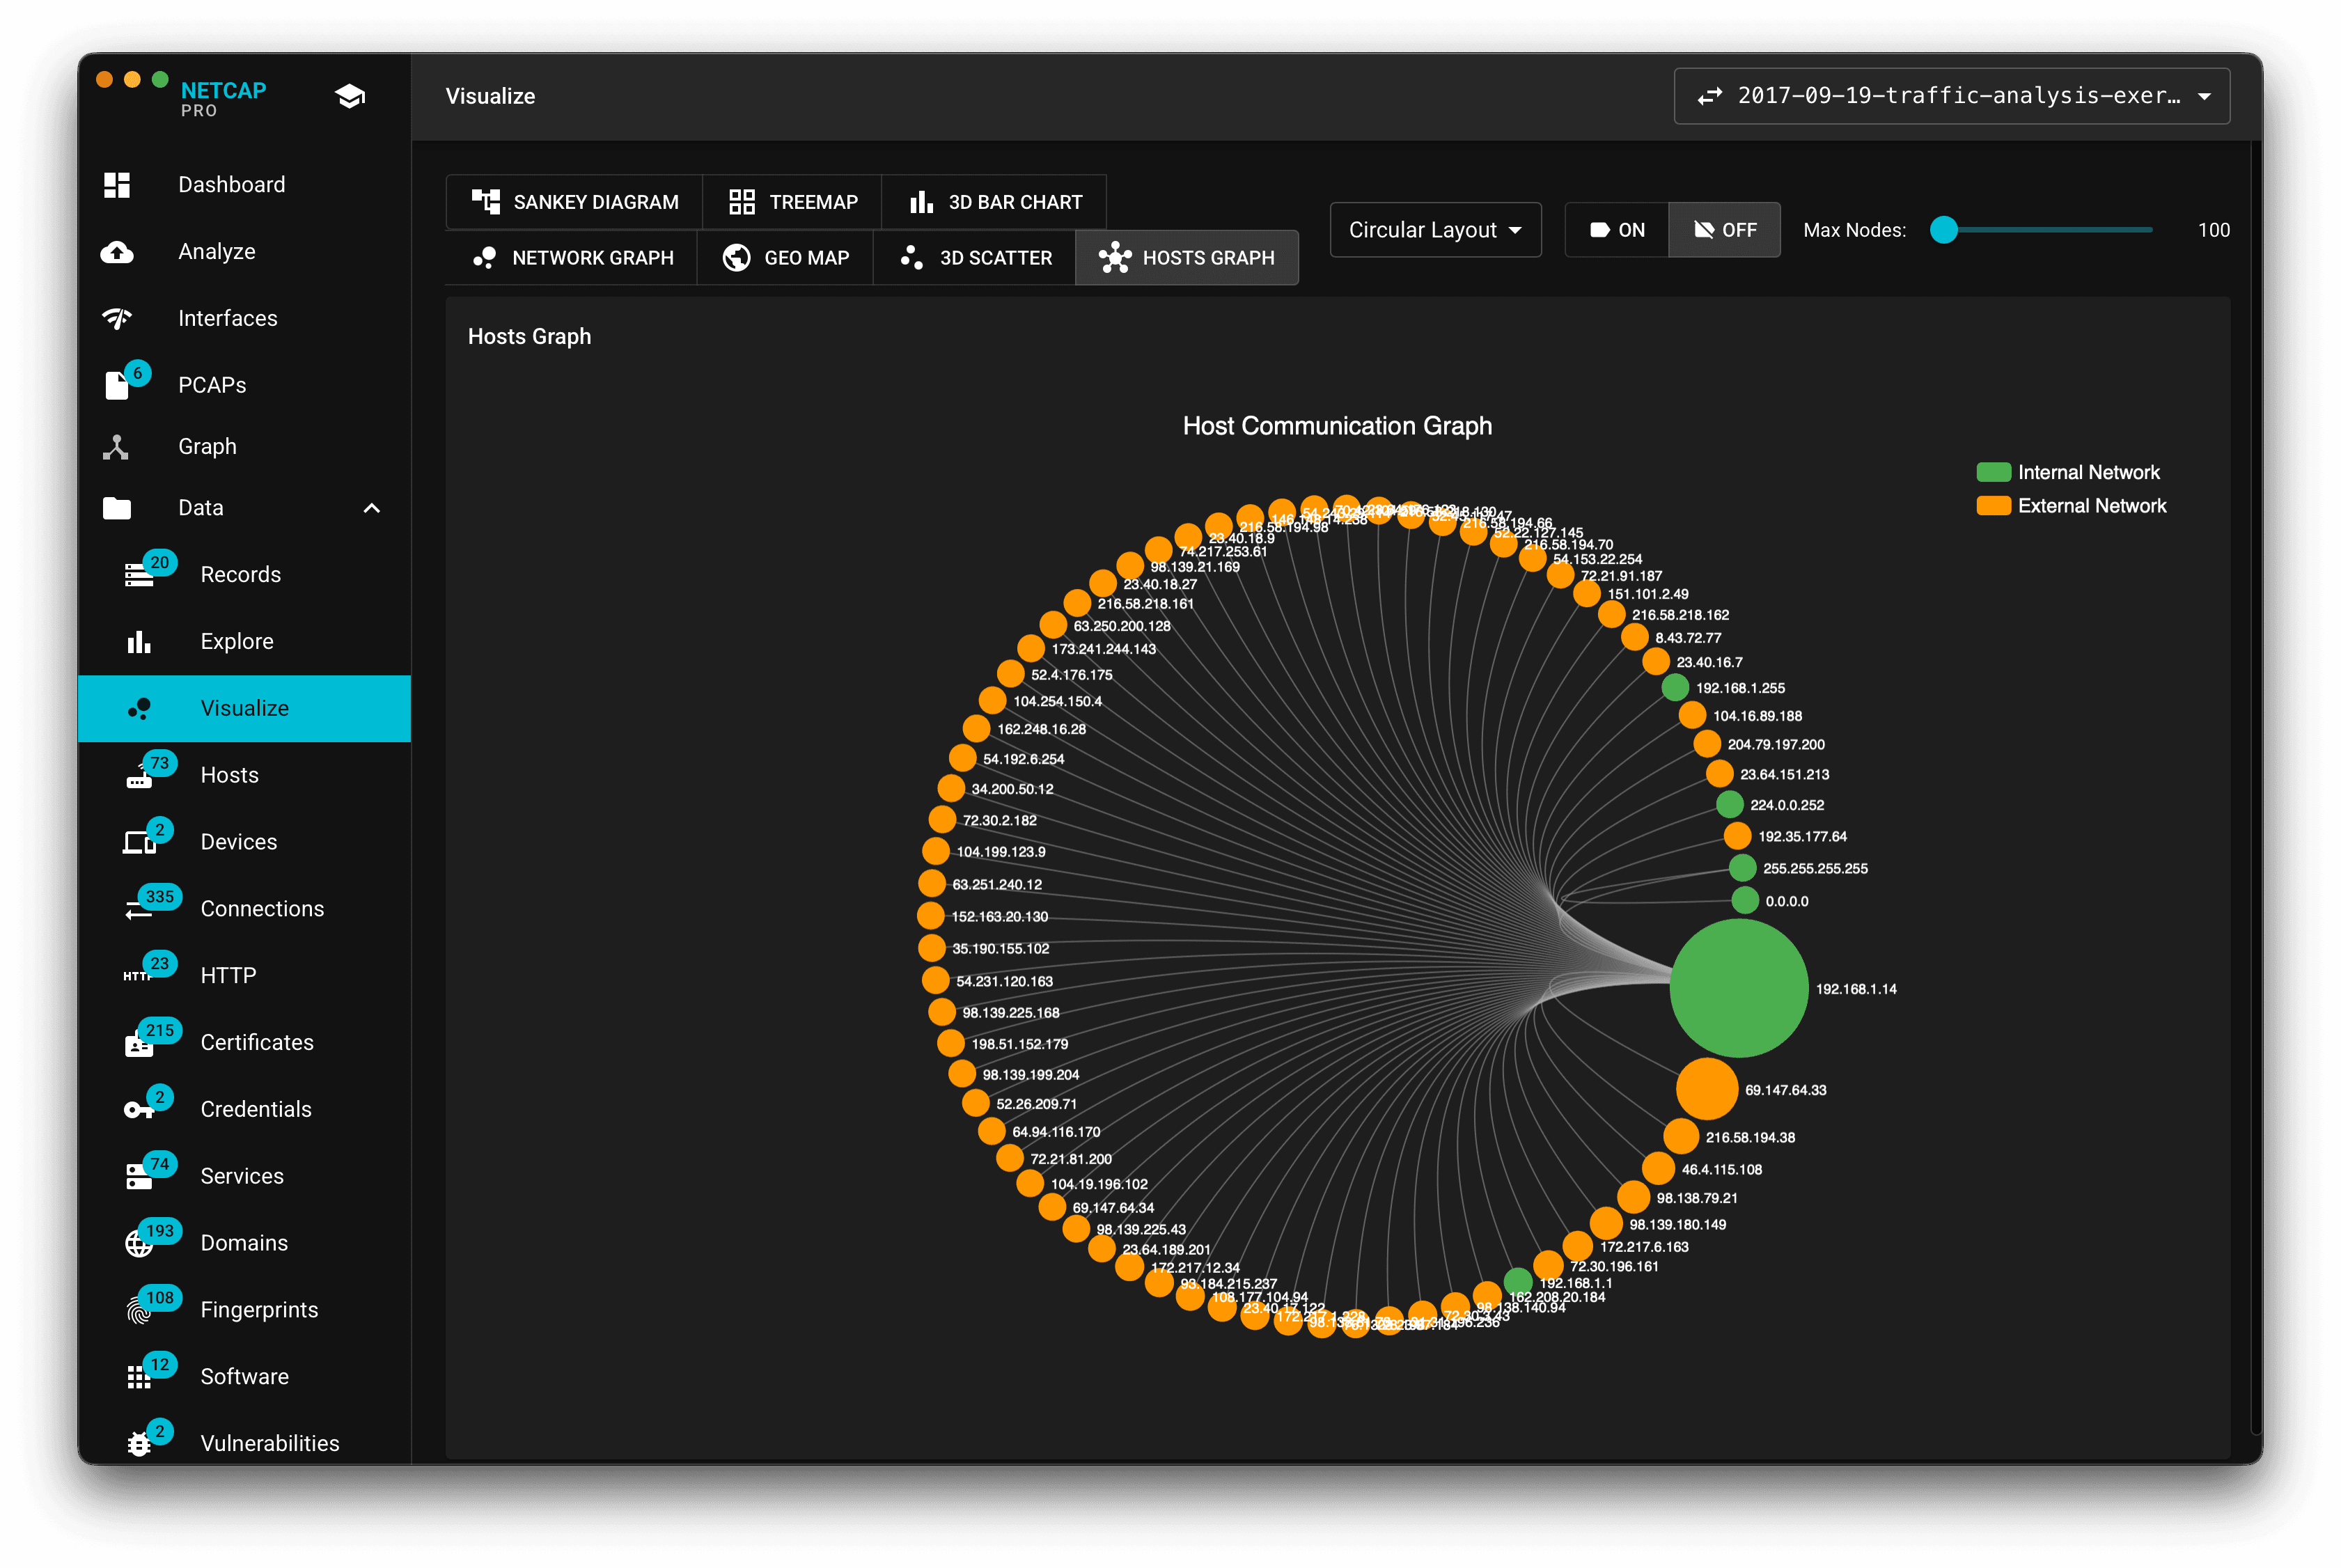
Transform packet captures into searchable records, connected visual evidence, and prioritized security findings.
Start with the open-source engine or use the complete desktop investigation workspace.
Trace a synthetic DNS and HTTP transfer through file extraction, a rule alert and a preserved packet selection.
Read the PCAP investigation workflow →Release notes, technical deep-dives and product updates. No spam, and you can unsubscribe at any time.